
OWASP ASVS Audit Report Template | Application Security Verification | Editable Word PDF Internal Audit Checklist
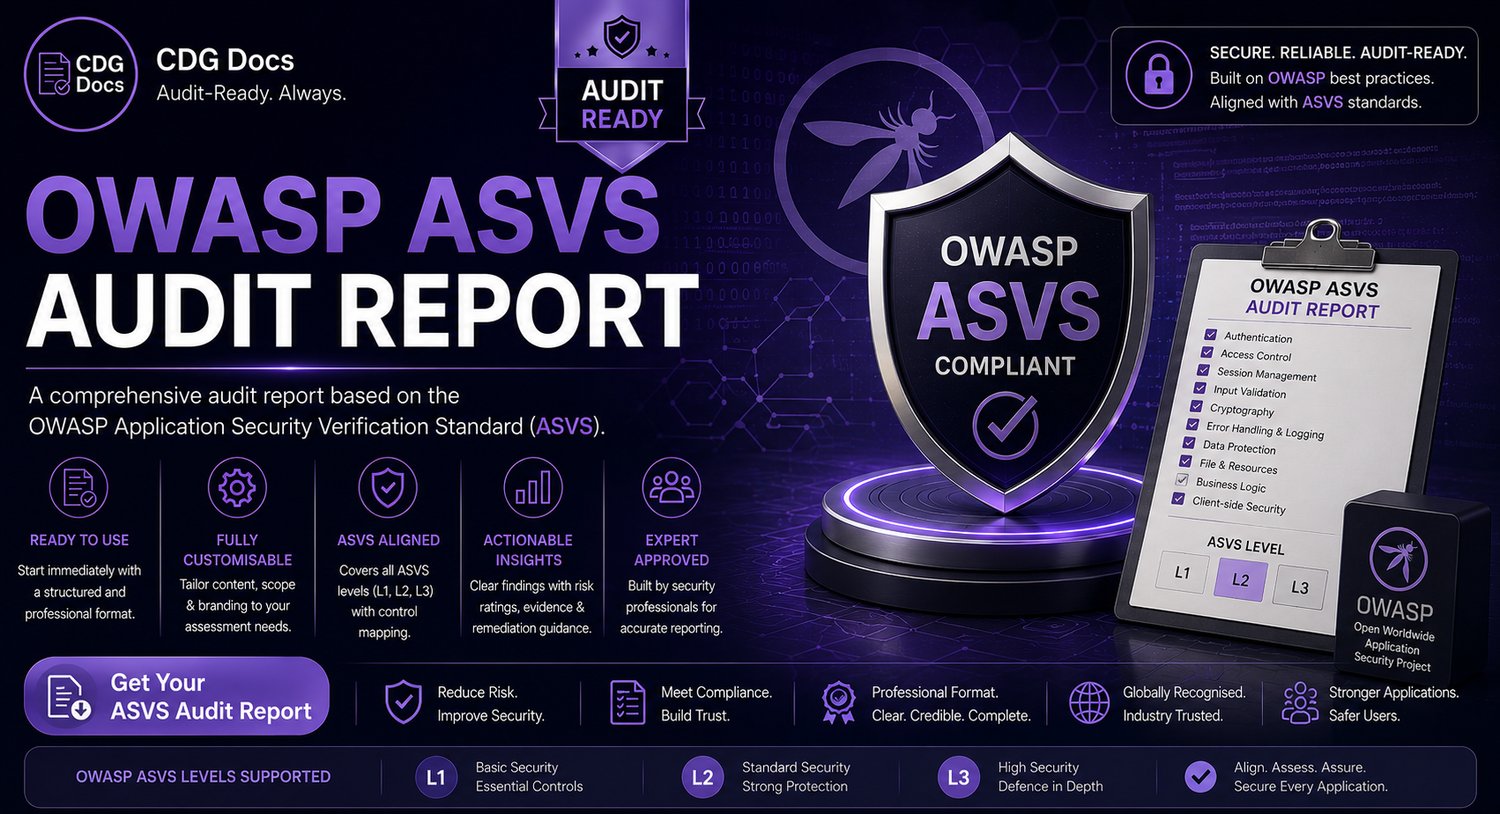
OWASP ASVS audits require structured documentation of application security controls, verification activities, testing evidence, security weaknesses, and corrective action follow-up—because secure software development depends on consistent validation against recognized security requirements. This OWASP ASVS Audit Report Format helps you streamline the audit process by capturing scope, findings, evidence, nonconformities, and CAPA in one professional report—so your application security assessment documentation stays consistent, complete, and audit-ready.
This is a ready-to-use, professionally designed, and fully customizable audit report created to streamline your audit process. It supports application security teams, software developers, DevSecOps professionals, cybersecurity consultants, auditors, compliance managers, and governance professionals by providing a standardized structure aligned with the OWASP Application Security Verification Standard (ASVS). Everything is organized to reduce reporting gaps, improve evidence traceability, and ensure corrective actions are tracked through closure.
Whether you audit web applications, mobile applications, APIs, cloud-native applications, enterprise software platforms, or secure development programs, this format supports stronger application security governance, improved vulnerability management, and clearer reporting for stakeholders.
What’s Included:
- Audit cover page and report header (application, version, audit period, auditor details)
- Audit scope, objectives, criteria, and OWASP ASVS reference section
- Application overview and architecture summary section
- ASVS verification level identification and assessment scope review
- Authentication and identity management controls assessment
- Access control and authorization verification section
- Session management and credential security review fields
- Input validation, output encoding, and injection prevention assessment
- Cryptography, data protection, and secure communications review section
- Error handling, logging, monitoring, and security event assessment
- API security and integration controls review fields (customizable)
- Findings and evidence recording fields (control-wise assessment)
- Nonconformity/vulnerability log with severity classification fields
- CAPA section (root cause, corrective action, owner, target date, verification)
- Executive summary, audit conclusion, management sign-off, and follow-up tracker
Key Benefits:
- Streamlines OWASP ASVS audit reporting with a standardized, ready-to-use format
- Improves application security documentation and evidence management
- Reduces reporting time with structured verification control assessment sections
- Supports faster remediation closure with clear ownership and due dates
- Strengthens audit trail quality for security reviews and compliance assessments
- Improves visibility into application vulnerabilities and security control effectiveness
- Fully customizable for web, mobile, API, and enterprise applications
- Ideal for AppSec teams, DevSecOps professionals, auditors, and cybersecurity consultants
Get your OWASP ASVS Audit Report audit report format today and streamline your audit process.